You Don't Even Have to Click an Ad: Zero-Click Spyware Attack Delivered Through Targeted Advertising Documented for the First Time
Citizen Lab has documented for the first time that simply loading an ad can be enough to infect a targeted device with spyware. Discover-Tech's ads appeared on 200,000 sites and apps, and at least 45 devices at Al Jazeera were targeted.
What did researchers find?
Citizen Lab, based at the University of Toronto, has spent years investigating spyware used by governments to monitor journalists and political opponents. In its new report, the team describes an attack technique it calls "AdFection": delivering spyware through targeted online advertising without requiring the user to click anything.
The report's main findings include:
- At least 45 devices at international news network Al Jazeera were targeted using this method in 2024 and 2025. Researchers attribute the attacks with high confidence to Israeli spyware company Candiru. Candiru's spyware was identified through network logs provided by Al Jazeera and a Windows file recovered from one device.
- The company buying the malicious ads was Israeli firm Discover-Tech, which presented itself as an ordinary advertising company. According to researchers, it was actually acting as a bridge between multiple spyware companies and the advertising ecosystem.
- Between March and June 2026, the company's ads appeared across roughly 200,000 different websites and mobile apps.
How can an ad carry spyware?
To understand that, it helps to look at how online advertising works.
An ad you see on a website or in an app is often the result of an auction that takes place in a tiny fraction of a second. The moment you open a page, information about your device — such as an advertising ID, IP address, location, device type, and the app you're using — can be sent to ad exchanges. Advertisers evaluate that information and bid for the chance to show you an ad, and the winning ad is then displayed on your screen. According to Citizen Lab, these auctions happen hundreds of billions of times every day.
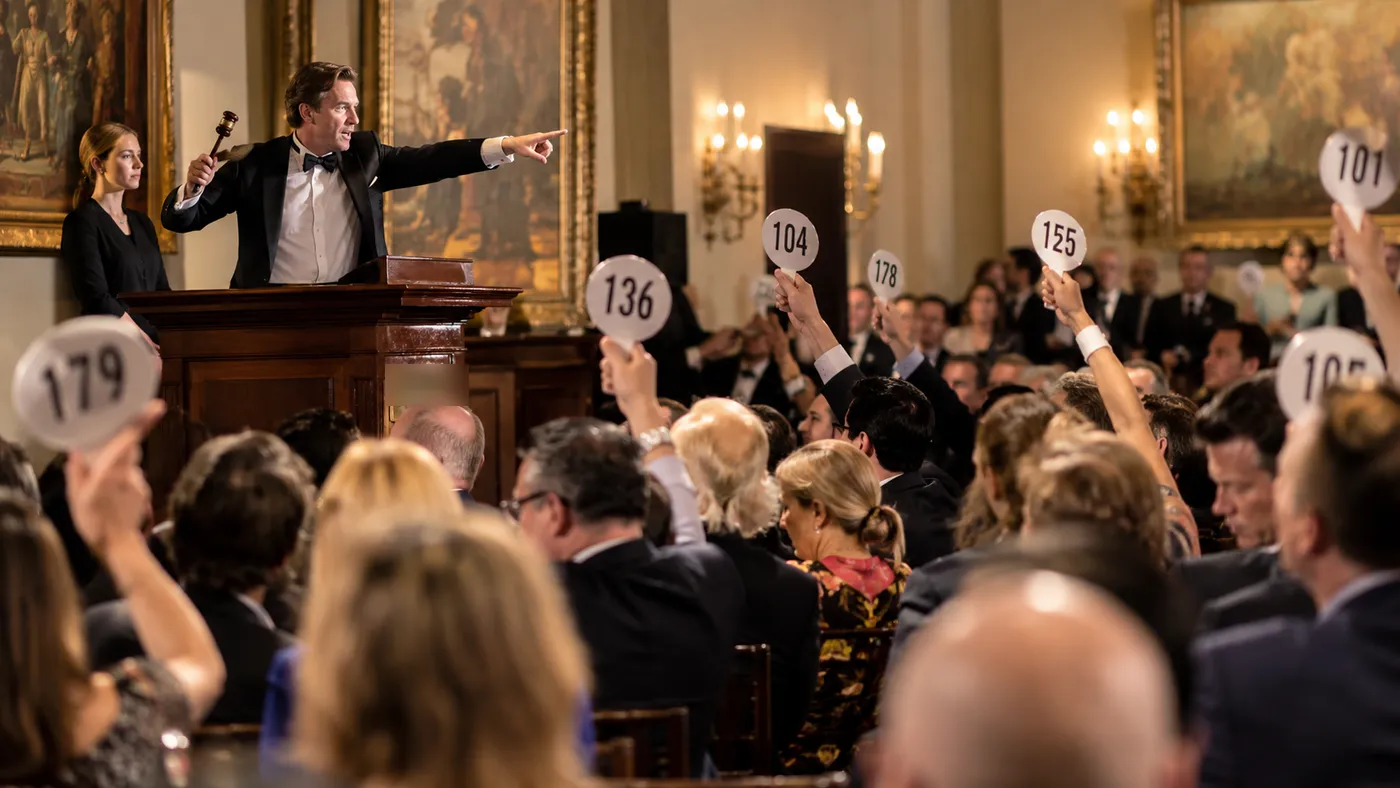
There are two critical points here:
First, the system carries enough detail to target a single individual. An advertiser can select a specific advertising ID or IP address as a target.
Second, an ad is not necessarily just an image. Ads can include code that runs inside the app or browser where they are displayed. Normally, that code is used to measure whether an ad was seen or clicked.
Discover-Tech's method combines these two features. When one of its ads loads on screen, it connects to the company's own server and sends device-identifying information such as the advertising ID, cookie identifiers, and IP address. The server then uses that information to decide whether the user is a target:
- If the user is not a target, it sends nothing. The ad appears completely ordinary.
- If the user is a target, it sends additional code to the device. That code redirects the device to infrastructure operated by the spyware company, where the device is checked and the spyware is ultimately delivered.
The advantage for attackers is that the malicious code is never shown to the advertising companies serving the ad. The ad networks see only an apparently harmless ad; the code that triggers the spyware is sent only to the selected target, and only once.
This is an important distinction from conventional cases of "malvertising." Malicious ads have long been used to redirect users to harmful websites or trigger security exploits. With AdFection, however, the advertising system's ability to target individuals is directly combined with a commercial spyware delivery chain. When the ad loads, it first connects to Discover-Tech's server; the next stage of the attack is then delivered only to a preselected target. This allows malicious code to be delivered without being exposed to ad platforms or non-targeted users.
Researchers also found that the company operated a control panel called "Controlium." The panel allowed customers to select specific people using advertising IDs or IP addresses and send them "controlled ads."
A company on trusted lists
Perhaps the most disturbing part of the report is this: from 2020 to 2026, Discover-Tech appeared on lists of "approved" advertising companies maintained by Google and the European advertising industry association IAB Europe. Its ads were distributed through major ad platforms including Google, Yandex, and Comcast-owned Beeswax. Researchers note that the company's links to the spyware industry could even be seen in publicly available corporate records.
Following notifications from Citizen Lab, Google terminated Discover-Tech's access to its advertising platforms. IAB Europe said it had suspended the company from its approved vendor list and that the new findings could justify permanent removal. Beeswax and several other advertising companies also blocked or suspended Discover-Tech's access.
One of the report's conclusions is clear: for years, the advertising system neither detected nor stopped this abuse.
How widespread was it?
It is important to distinguish between two things here: an ad being displayed and spyware actually being installed.
Discover-Tech's ads appeared across a very broad area. Researchers examined roughly 4 billion bid records from a four-month period. Ads containing script tags that connected to Discover-Tech's attack infrastructure appeared in more than 75,000 mobile apps and more than 120,000 websites. These ads also appeared on networks belonging to NATO, the United Nations, European Union institutions, government ministries in multiple countries, major technology companies, and media organizations.
However, as the researchers emphasize, an ad appearing on a device does not mean that the device was infected with spyware. In the vast majority of cases, the server sent no code at all. Even so, the ads collected information from every device on which they appeared; the report states that millions of devices were directed to connect to infrastructure associated with the spyware company, likely as part of large-scale tracking and reconnaissance.
This kind of spyware typically targets specific individuals, such as journalists, activists, politicians, and government employees, so the average user is unlikely to be directly targeted. But the report demonstrates how the same advertising infrastructure used by everyone can also be repurposed for these attacks.
What can you do?
There is no complete protection against highly targeted attacks like these, but there are steps that can reduce the risk and are good security habits in general:
- Keep your device and browser up to date. These attacks ultimately have to exploit a security vulnerability in the device or browser. Updates patch known flaws.
- Limit your advertising identifier. On iPhones, you can prevent apps from tracking you; on Android, you can delete your advertising ID. This makes it harder to identify and target you as a unique user through advertising systems.
- Consider using an ad blocker in your browser. Preventing ads from loading also removes the delivery channel used by attacks of this kind.
- If you work in a high-risk profession, consider additional protections. Journalists, activists, and people in sensitive roles can use options such as Apple's Lockdown Mode and Android's Advanced Protection features.
Citizen Lab's report shows that online advertising is not only a privacy issue, but also a security issue. For years, we have been told not to click suspicious links. This report is a reminder that sometimes you may not need to click anything at all — the attack can arrive inside an ordinary-looking ad in the corner of your screen.
Related posts
All postsHackers Set Supermarket Refrigerators to 50 Degrees: Cyberattacks Are Reaching Into the Physical World
Hidden Listening Device Found in OpenAI Meeting Room: Prosecutors Say AI Was Involved in Nearly Every Stage of the Plan
.agent and .agi Could Join .com: The Internet Is Expanding Again After 14 Years